Security
Vetted technology. No open-source hacks and cracks.
eCommerce demands security, no matter how tirelessly a platform is marketed or how popular it becomes. The SoNET Web Engine is one proprietary engine, with no third-party plugins for attackers to target.
How a generated site is protected
Security built into the engine itself.
Content is cleaned on save
Scripts, event handlers and javascript: links are stripped from everything saved in the editors, so a page cannot be turned into an attack on its own visitors.
The admin stays closed
Visitors who are not signed in are sent to the login for every admin address, and edit modes do not exist for them. Repeated failed logins lock the account.
Payments never touch the site
Card payments are collected by major processors (PayPal, PayFlow, Authorize.Net, Elavon) on their own secure hosted forms, in line with PCI SAQ-A requirements, and the payment integration code is not open source.
No plugin supply chain
Every feature is part of the engine. There are no extensions from unknown authors to install, update or forget.
Spam and abuse controls
Picture captchas protect forms and comments, comments can be switched off, and sites can be made members-only.
Privacy and recovery
Visitor Insights work without tracking cookies, sign-in supports OAuth 2.0, and the entire site can be backed up.
On the record · May 2020
Open source platforms, by their vulnerability record.
Open source web solutions have been marred by security vulnerabilities, and backdoor hacks and cracks are found in them regularly. These listings from CVE Details, the security vulnerability data source, were captured in May 2020 and first published on this site.

WordPress

Joomla
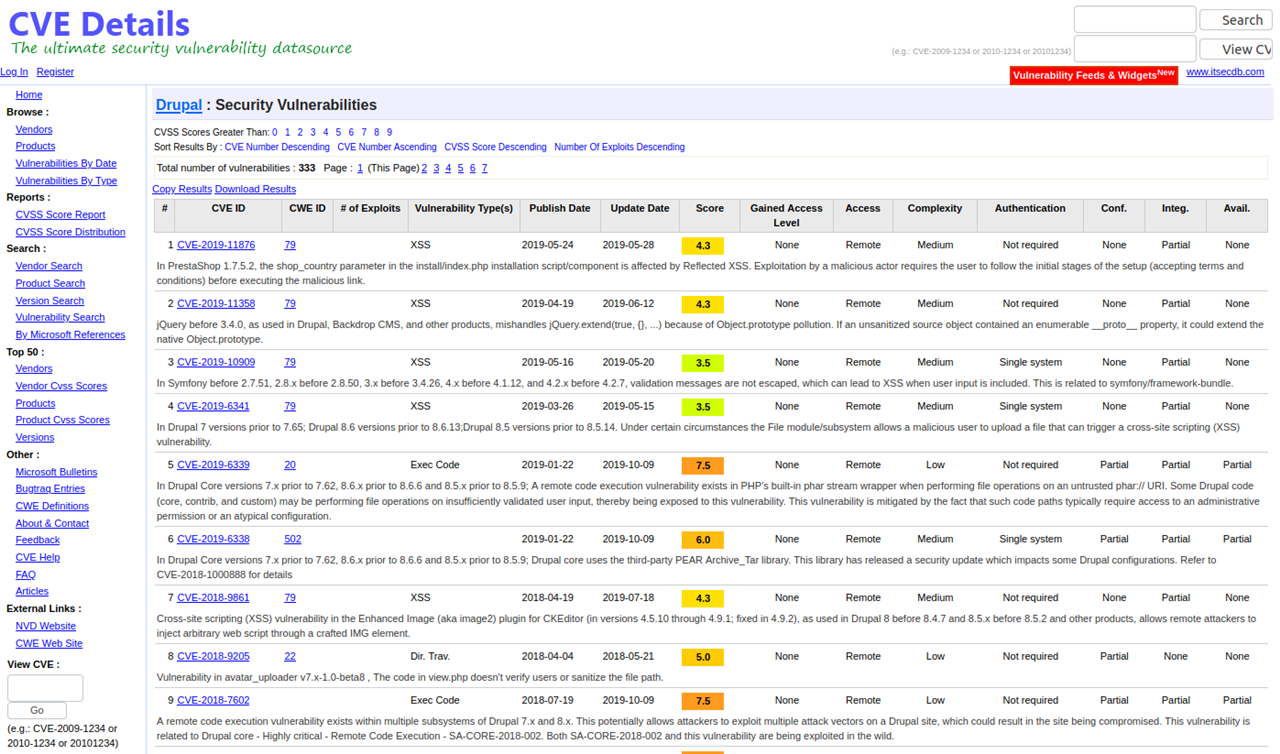
Drupal
#FactsMatter. Switch to a platform built for secure eCommerce: instantly create a secure eCommerce website.